Tool · Private
REToolKit
Reverse engineering has always fascinated me, because every
program is open source to someone who knows how to read it.
REToolKit started as my way of learning assembly and how programs
work at the lowest level, and it grew into a tool that automates
as much of the work as I could. The automation is built in and runs fully offline, no
extra tools needed.
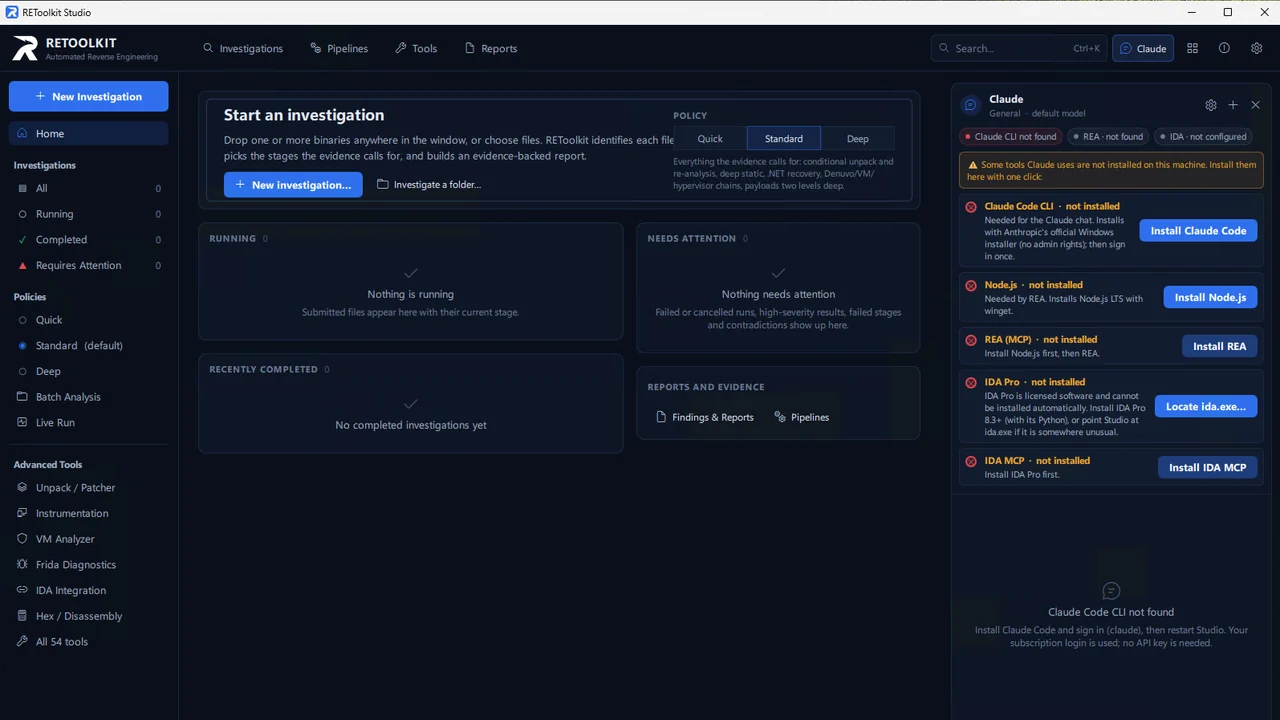
Drop in one or more programs and it identifies each file and picks
the analysis steps the evidence calls for, from unpacking to .NET
recovery to virtualised code. It runs suspicious code in an
emulator inside a closed sandbox to see what it actually does
without risking your machine, and that's just one of many steps it
handles on its own. The result is a report where every finding is
backed by evidence, with verdicts that match what industry-standard
antivirus software reports. 54 tools, all in one app.
When you want to go past the verdict, Claude takes over. REToolKit
hands it the full investigation as context, so it works through
the binary like an analyst who's already been briefed. It drives
IDA Pro, REA and Frida through their MCP servers, gathers what each
one finds into a single context, follows up wherever it can and
explains it all in plain English.
I planned to release it as open source, but it's become powerful
enough that I decided to keep it private.